Calibrated audits for AI-native companies.
Throughline is a registered CPA firm and Certification Body specialising in AI-native companies and AI-centric services. We conduct independent audits calibrated to how your company actually operates.
Sydney headquartered CPA firm serving Australian and US companies
Growth, operations and risk, connected as one thread. That's your throughline.
The predictable issues that come from generic audit programs.
When the audit follows a template rather than your business, you tend to see the same four things:
Calibrated to the company you actually are.
Compliance, by nature, is the minimum expected at your stage. Your security, your service standards and your product already go further than that. Compliance just needs to go far enough to match your risk profile and what your customers reasonably expect.
When the program fits, you stop maintaining two systems: the real one that runs the business, and the one built to satisfy an auditor. They become the same system, and what you show an auditor is simply what's true.
Your goals, commitments and stage set how far your controls need to go. Your technical scope determines which controls apply and how to evidence your compliance.
Multiple frameworks, seamlessly connected.
The baseline of enterprise information security expectations.
Information security management system certification.
AI systems certification for responsible AI.
European data privacy rights and the global privacy benchmark.
The global benchmark for healthcare data protection.
Controls required for SOX and financial reporting.
ASAE 3150 assurance for CDR accreditation in Australia.
Not mutually exclusive. Most scaling companies end up with two or three, run as one program. SOC 2 vs ISO 27001 →
Four things you can count on, on every engagement.
A named senior practitioner leads your engagement from scoping through report issuance. No handoff to a rotating junior team.
We calibrate each audit around four inputs: stage, system scope, service commitments and compliance goals. That includes how your AI operating model actually runs the business.
We stand behind our work with a service guarantee and support your enterprise conversations, so buyers trust and act on your reports.
Available when your team has capacity, not on a rigid schedule. Engaged as your business changes, not just at audit time.
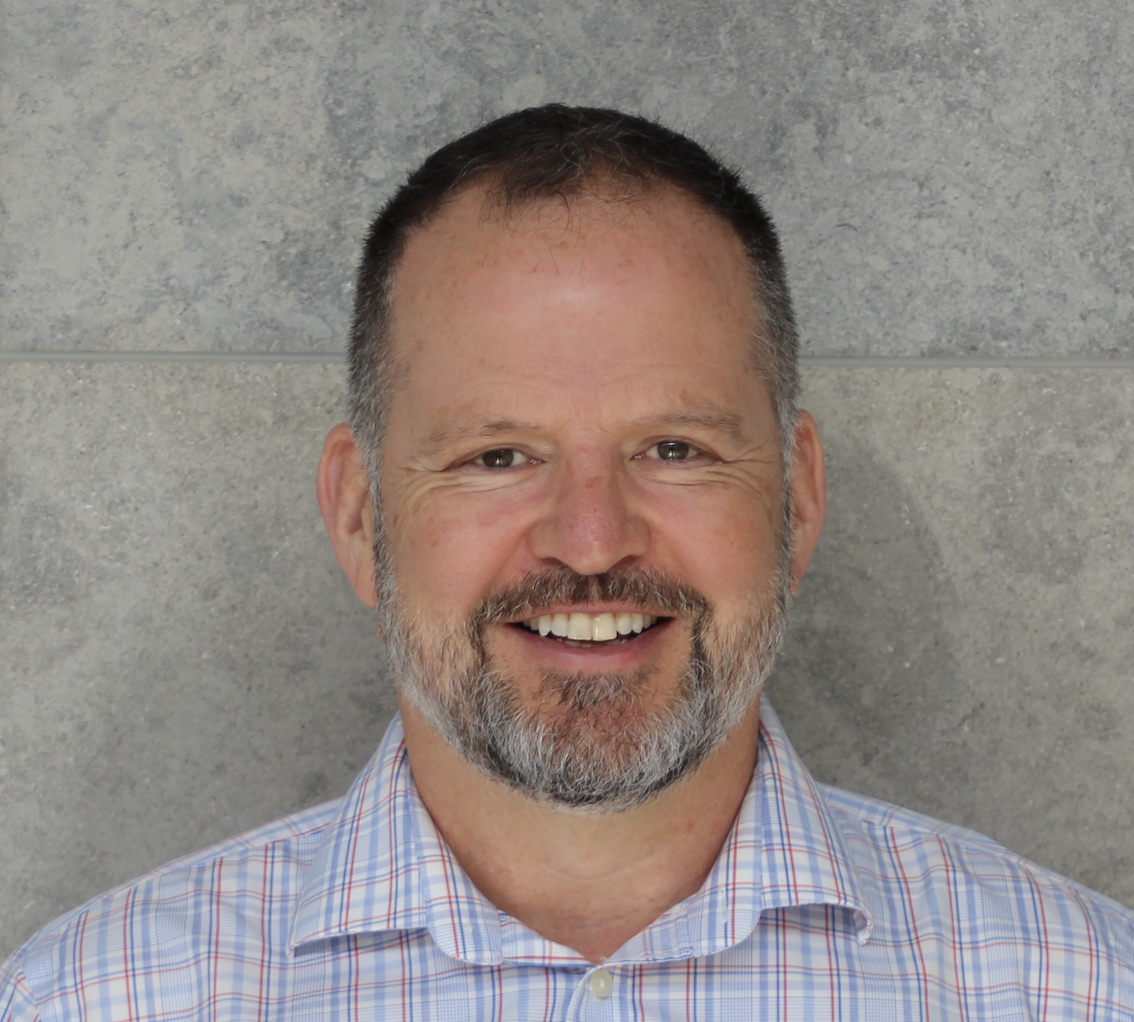
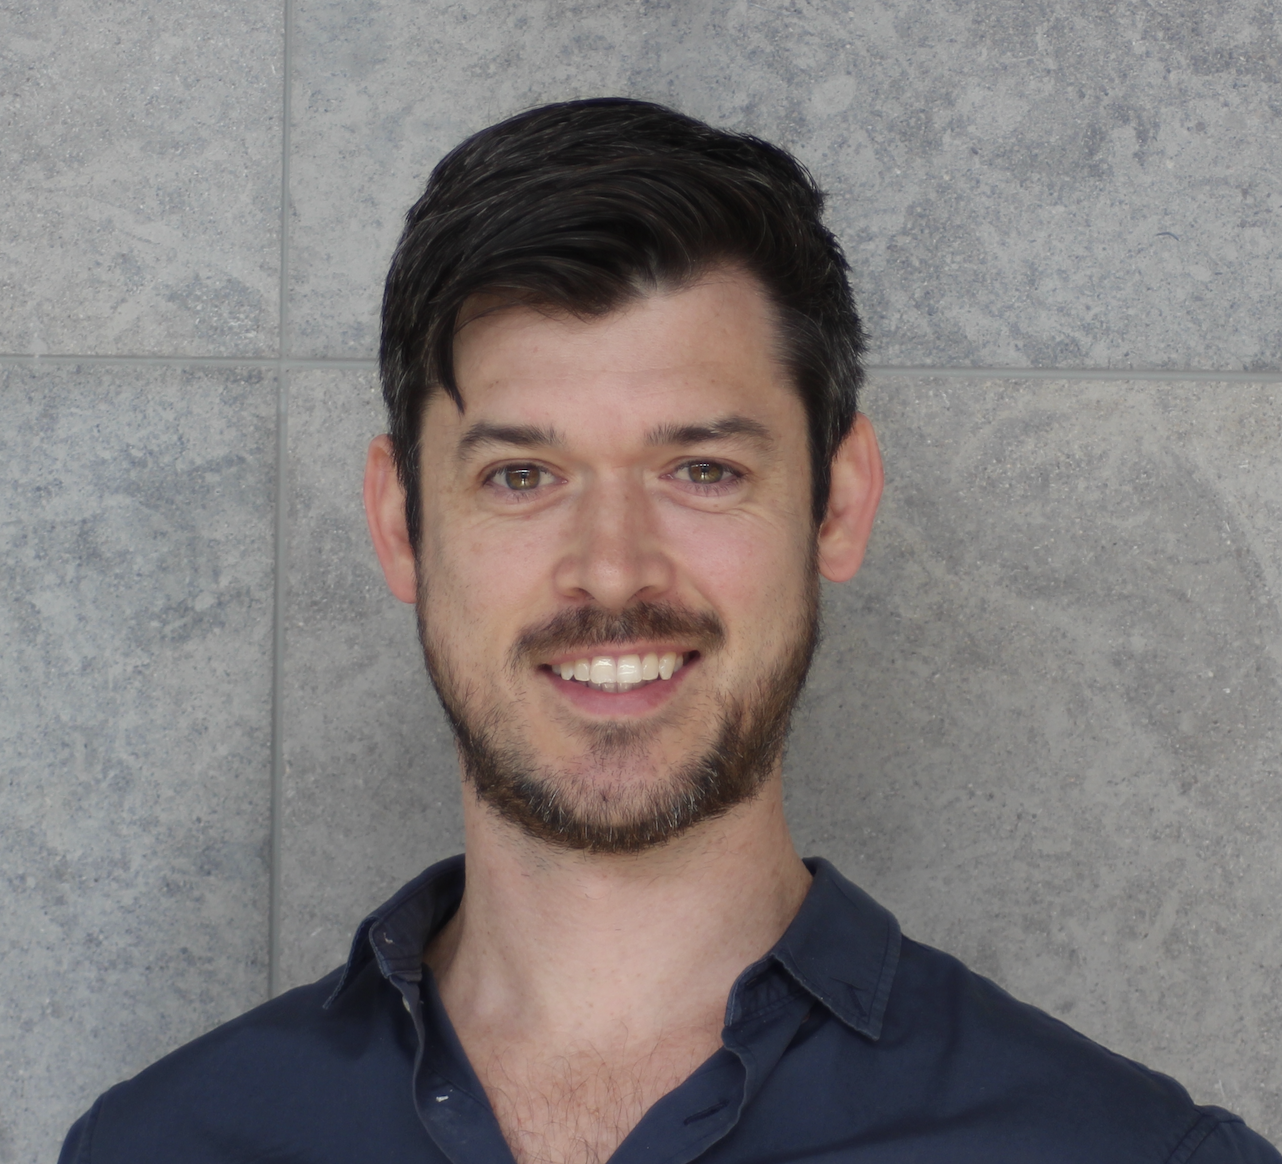
Experienced practitioners, close to the work.
Rob McAdam and Paul Wenham have each built market-leading firms in cybersecurity and compliance. Rob founded Pure Hacking, CXO Security, and Sekuro. Paul founded AssuranceLab, before its acquisition by Sensiba.
They are applying those lessons to the next era of assurance: AI-native operations, AI-centric services and agentic compliance. Every engagement has a named senior practitioner accountable from scoping through report issuance.
The questions we hear most often.
Ready when you are
Compliance that fits the company you actually are.
Start with a complimentary Compliance Strategy Workshop with a senior practitioner.